A customer sent a security questionnaire
A bigger deal depends on answering questions about access control, encryption and testing, and you’re not sure what the honest answers are.
We help teams find and fix security problems in their applications, cloud accounts and delivery pipelines, then add the checks that stop the same problems from coming back. It’s practical work aimed at reducing real risk, not at producing paperwork.
Security work rarely starts with a plan. It usually starts with one of these.
A bigger deal depends on answering questions about access control, encryption and testing, and you’re not sure what the honest answers are.
API keys and passwords live in code, environment files or chat messages, and nobody is sure who can see them.
Broad permissions were easier at the start. Tightening them now feels risky, so nobody does it.
The application has grown a lot, but no one has looked at it the way an attacker would.
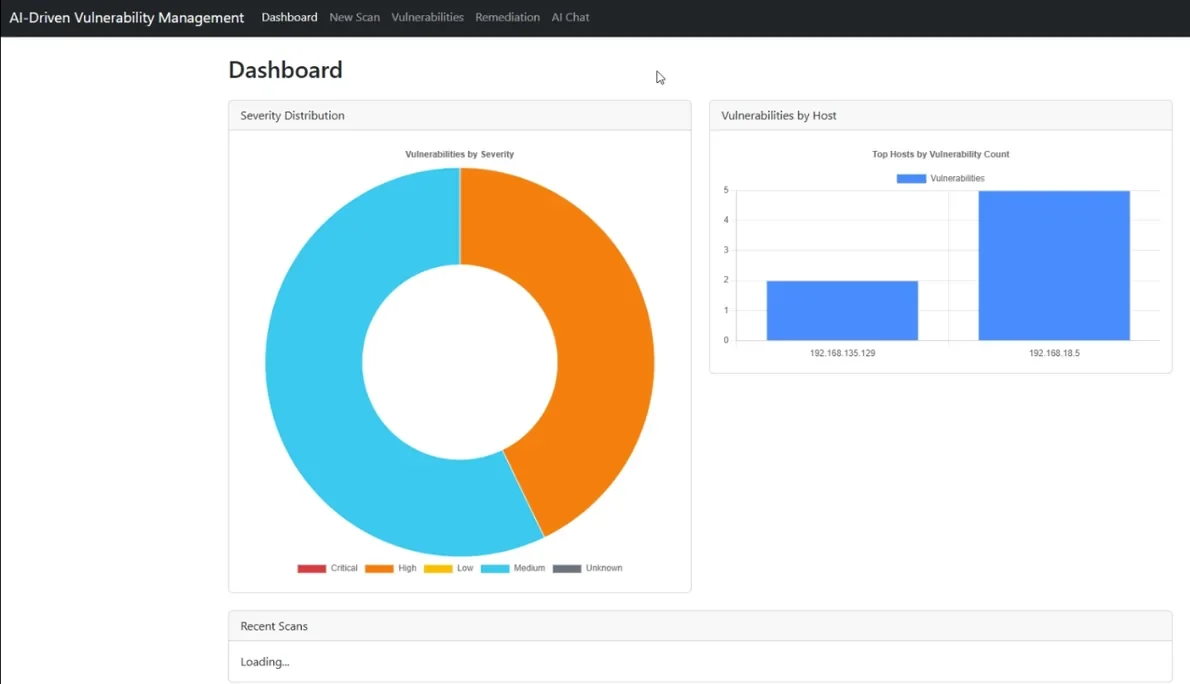
Tools produce long lists of warnings, and the team can’t tell which ones actually matter.
Reviews happen at the very end, find problems late and turn into arguments about deadlines.
Pick one piece or hand us the whole thing. We’ll suggest where to start after we understand your setup.
We test web applications and APIs against the OWASP Top 10 with tools like OWASP ZAP, then confirm each finding by hand so you only deal with real issues.
Dependency, container and code scanning are added to your pipeline and tuned to catch real problems without blocking every build.
We review who can do what, move you towards least privilege and put secrets into a proper secrets manager.
We check your AWS accounts for public storage, open ports, weak logging and other common misconfigurations.
Hardened images, tighter network rules and safer runtime settings that limit what an attacker could reach.
We set up monitoring with tools such as Wazuh and Grafana, so suspicious activity gets noticed instead of buried.
You get a clear picture of where you stand, a practical plan to fix it and proof that the fixes worked.
Don’t see your question here? Ask us on a call or send it with your project details.
It overlaps a lot. Our assessments cover the OWASP Top 10, API security and authentication. If you need a formal pentest certificate for compliance, we’ll tell you upfront and can help you get ready for it.
We agree on scope and timing with you first and prefer to test against staging. When production testing is needed, we keep it careful and coordinated with your team.
Yes. Many clients ask us to handle the fixes as well, and we finish with a retest so you know each issue is closed.
We don’t issue certifications, but much of our work, such as access control, logging and secure delivery, is exactly what auditors look for. We’re happy to work alongside your compliance advisor.
Our team holds the ISC2 Certified in Cybersecurity credential and has hands-on experience with SIEM, intrusion detection and vulnerability management.
Book a free 30-minute discovery call, or send us a few details and we’ll reply within one working day.